Do I still need to write the new Secure Boot certificates to the UEFI? In Windows, the Device Security section doesn't show that the certificates have been applied.
No, that's not necessary. Since your PowerShell commands
[System.Text.Encoding] : : ASCII.GetString((Get-SecureBootUEFI db).bytes) -match 'Windows UEFI CA 2023'
and
[System.Text.Encoding] : : ASCII.GetString((Get-SecureBootUEFI db).bytes) -match 'Microsoft UEFI CA 2023'
already showing the status "True". This indicates that the new secure boot keys 2023 for Windows and Linux are already registered in the UEFI.
We outsmarted the MS restriction, but Windows "Device Security" didn't notice!
It is a stupid tool and still warning that Win Updates will not install the new Secure Boot Keys 2023 automatically as your PC has no TPM2 Modul within your CPU. Even though your new Secure Boot keys 2023 are already present in the UEFI!
1 Like
When I enter
sudo mokutil --kek
on my Dualboot system in Zorin, there is only shown the 2011 certificate that is valid until June 2026 although in Windows both power shell outputs showed true.
sudo mokutil --db
shows certificates which are valid until 2035 and 2038.
Is that normal?
Bluescreen after an update for the new secure boot certificates on my HP Notebook Elitebook 840 G10 with Windows 11:
Really annoying! Bitlocker was not enabled. You seem to have to resize the 100 MB EFI partition because it is too small...I had to turn off secure boot to be able to boot.
https://www.reddit.com/r/msp/comments/1u24ii5/bsod_0xc0430001_error_with_new_kb5094126_on/?tl=en
I updated the BIOS to the latest version and followed a post in the reddit link to move a folder of the efi partition to C:
"
mountvol Y: /s
mkdir C:\Install\HPDEVFW
move Y:\EFI\HP\DEVFW\* C:\Install\HPDEVFW\
mountvol Y: /d
"
Then the problematic update KB5094126 worked (but only with secure boot still disabled), and afterwards I enabled secure boot again and the laptop booted  .
I'm completely new to commands like this in Windows. Does anyone know if I need that folder and if I have to move it back to the EFI partition? If yes, which commands are required? I'm guessing it probably won't fit in the 100 MB EFI partition now, or? However, I've never expanded the EFI partition in Windows before—the Windows partition is right behind it, so there's no space there.
Windows security now shows that all necessary certificate updates have been applied. Still, it was a nightmare!!
You could try it with GParted. You make some free Space of the Windows Partition at the Beginning or at the Ende and move it to the Beginning. And then expand the EFI-Partition.
1 Like
I read so many times that an EFI partition of 100MB is to small for the update so I just expanded the partition to 500MB using 'MiniTool Partition' on my 8 year old desktop pc with a plugin TPM2 module.
I wonder why I did it when you see how much is actually used with all new keys /certificates applied...
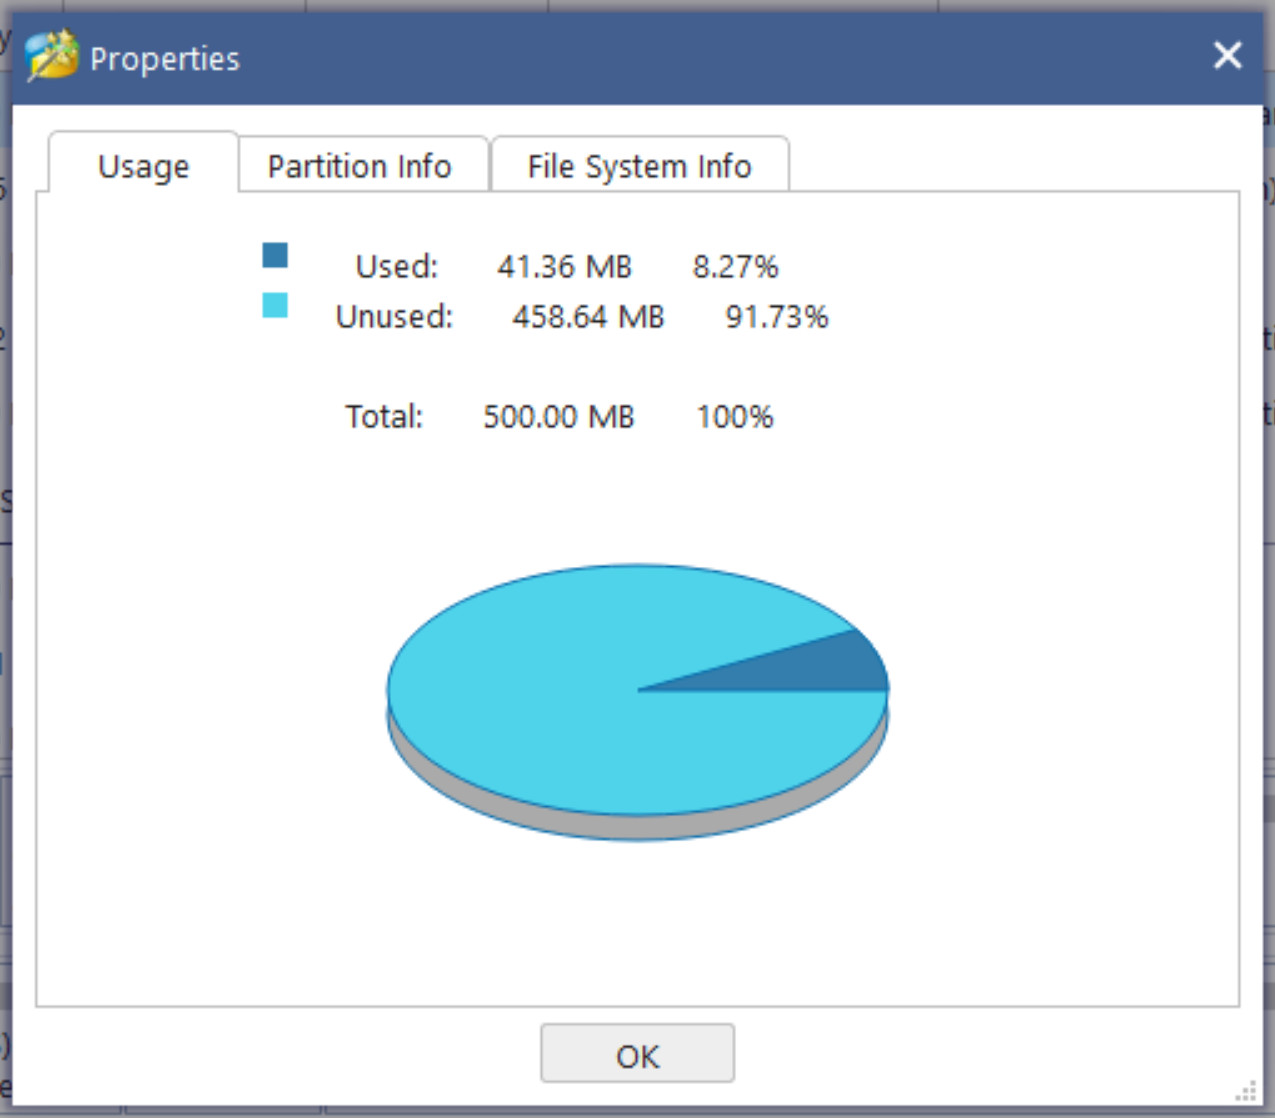
Probably the actual reason was that I had secure boot disabled.
Unfortunately, I wasn't able to extend the partition because a 16MB "system-reserved other" partition created by Microsoft was in the way. None of the free tools could move it. I could have just deleted it, but I didn't dare to do so because I didn't know if I might need it.
So now I’ve reinstalled Windows 11. I’d hoped there would be a manual partitioning option, but that wasn’t the case. Fortunately, though, 25H2 created an EFI partition that’s 200MB in size and all the updates - including the one that caused problems yesterday - installed without a hitch. So much work, all because of a stupid update.
1 Like
Sorry, @swarfendor437 . It's been hectic here and I've only just logged back in.... Yes, it's all in the original post. I guess you've read all about it by now.
 Nope!
I think the simplest solution is change BIOS settings to Legacy Boot and forget about Windows.
Sorry for the very delayed answer...
The 2 PS commands you used on the win admin terminal to implement the 2023 secure boot keys within UEFI just did the same as MS initiates during Win Update: In each case, the complete installation of the new 2023 DB Authorized Signature Database database keys as well as the 2023 DBX Forbidden Signature Database database KEK key is requested.
But in your case as on other older hardware BIOS / UEFI firmware can't handle the new 2023 KEK key for the DBX database. This means, that in this case no more new entries (for example future additional discovered malware bootkits) can be written to the DBX database.
As your PC (and many other older hardware) has no available firmware update including the 2023 KEK key, there are no more options to write new entries into the DBX database working after 2011 KEK key is expired. Thenceforth the "Black List" stays unchanged.
2 Likes
Does that mean it's best to just leave Secure Boot disabled, since it doesn't really provide much protection anyway?
This is where the confusion for all of us lies. Let's look at the history. EFI was introduced because the BIOS is vulnerable to bootkits. If you have an old machine, then it won't suppor EFI and in addition won't support TPM 2.0.
EFI/UEFI was not a Microsoft invention 'per se', but they just control the certification process which is the biggest bug bear.
1 Like
MS usually sends the new DBX entries over win updates over the same way as the 2023 secure boot keys.
Without the 2023 KEK key the protection against bootkit malware includes only the status of the DBX entries maximum until expiring 2011 KEK key. Or only until Win10 end of support Oct 2025? Never for older CPUs without TPM2.0?
It is questionable as you didn't get the new secure boot keys 2023 via win updates, why should MS provide you with new DBX malware entries even the KEK 2011 key was still valid as you didn't get the 2023 secure boot keys over win updates at all?
MS shows that security of their customers is for them only a smoke grenade. This is a really MS non professional behavior to their (not longer) customers.
The meaning looks like: if you want to use MS arbitrarily restrikted hardware, you can in circumstances not use any other OS on this hardware. You are lucky if you can disable secure boot in BIOS / UEFI as it is not possible on all firmeware. And many people don't know how to disable it even it would be technical possible.
More and more new computers come with secure boot enabled and can not be disabled, for example the Secured-Core-PCs. Often it is not visible for the buyer. It might be useful for bigger companies, but for private users it can be a MS trap special for laypersons.
1 Like